
When Legal Says "No," What Are They Actually Worried About?
I have been asked this question a lot lately. Mainly because design teams have started using AI tools for proofreading, color matching, and layout work. Then one day, legal or the boss shows up and says, "You can't put customer data in there."
Legal's concern is not pointless. The public version of ChatGPT, meaning the version you open in a browser and log into directly, has one key behavior: by default, the content you enter may be used by OpenAI to improve its models. This is not a secret. OpenAI's privacy policy says it clearly. Most people just never read it carefully
Where exactly is the problem? If you paste a quote confirmation sheet containing a customer company name, contact person, and purchased items into ChatGPT and ask it to polish the wording, that data has been sent to OpenAI's servers. From a legal control standpoint, the data is no longer only in your hands
Taiwan's Personal Data Protection Act requires companies to have a specific purpose when collecting, processing, and using personal data, and they must not go beyond the necessary scope. Sending customer personal data to a third-party AI platform crosses that line, strictly speaking, unless you informed the customer and obtained consent when collecting the data. In B2B printing sales, almost nobody does that
That is the line legal is drawing when they say "no." They are not just making your life difficult
What Is the Difference Between Public AI and Enterprise AI?
Banning AI across the board is the other extreme. It is also unnecessary. The key is understanding what kind of AI you are using, because the level of data isolation is completely different
Public version (Consumer tier)
・Free ChatGPT and Plus personal accounts: input data enters the training pool by default, unless you manually go into settings and turn off the "improve the model" option
・Suitable for personal use and creative brainstorming that does not contain customer-identifying information
Enterprise and API versions (Enterprise / API tier)
・ChatGPT Enterprise and Microsoft 365 Copilot through Azure OpenAI: OpenAI clearly commits that it does not train models on Enterprise customer data, and data is encrypted both in transit and at rest
・API calls, when the user parameter is set and the account is confirmed as part of an API plan, are also covered by the no-training policy
Local deployment
・Running open-source models, such as the Llama family, in your own server room or private cloud: data never leaves your environment, so compliance risk is the lowest
・The downside is IT setup cost. This suits printing plants or design companies with a certain scale
Put plainly: even though both are called "AI," the fate of your data is very different in the public version and the enterprise version. When many companies say "AI cannot be used," what they should really say is "public AI cannot be used to process customer data." Those two statements are very different
Variable Data Printing Is Far More Sensitive Than Most People Think
Variable Data Printing, or VDP, is the scenario in the printing industry that calls for the most caution
In simple terms, VDP means each piece in the same print run carries different names, addresses, barcodes, or personalized content. Direct-mail envelopes, membership cards, insurance policies, and medical report covers are all typical VDP applications. The nature of this work is that you will definitely have a large list of personal data in your hands
I have seen a very common situation: to check whether a VDP template is laid out correctly, a designer pastes an entire CSV containing 500 customer records into an AI tool and asks it to "check the field format." Just like that, the names, addresses, and phone numbers of those 500 people are sent out
For VDP work, the recommendation is simple: always use de-identified fake data for template testing. From the moment the real customer list enters the workflow, it should only run in an environment with information security controls. It must not touch public AI tools
If you need AI to help improve the design logic or layout rules for VDP, write the rules out in text, such as "the name field can contain up to 8 Chinese characters, and if it exceeds that, reduce the font size to 8pt." Send the rules to AI, not the real data
Which Data Can Be Used, and Which Data Must Be De-identified First?
This is the question people ask most often in practice. A simple classification looks like this:
Can be put directly into AI (low risk)
・Public information, such as product specifications, material introductions, and descriptions of printing methods
・Fully fictional design copy, such as Lorem Ipsum for testing or fake data you wrote yourself
・Internal process documents that do not contain any identifying information about customers or employees
・Technical questions, such as "What is the standard CMYK value for Pantone 485C?"
Must be de-identified first
・Customer requirement documents: replace the company name with "Customer A" and the person's name with "purchasing contact."
・Past case references: blur all specific identifying information in the case before describing it
・Draft quotes: item names and specifications can stay, but the customer name, tax ID, and purchaser name must be removed
Never put into AI (high risk, regardless of AI type)
・Any list containing a natural person's name, phone number, address, or national ID number
・Original design files or brand guideline documents covered by a confidentiality agreement with a customer
・Financial data, contract terms, and detailed quote breakdowns, especially for competitive tenders
・Employee salary, performance, or HR data
The core rule for de-identification is simple: after removal, no one should be able to infer the real individual or specific company from the remaining data. Merely changing the name while keeping a distinctive business description is not true de-identification
If you need AI help preparing a printing proposal, consider discussing with the Mai Strategy Knowledge Academy consulting team how to build a legally compliant AI workflow, especially for data classification rules in VDP and commercial printing scenarios
What Clauses Should You Check When Signing an NDA with an AI Vendor?
Many companies look only at features and price when adopting AI tools, then skim over the confidentiality agreement. This is a very common mistake
A trustworthy AI vendor NDA or service terms should cover at least the following points:
Data use
・Does the vendor clearly commit that input data will not be used to train models?
・Is there a clear data retention period, such as deletion within 30 days after processing is complete?
・Will the data be used only for the purposes specified in the contract, with no disclosure to third parties?
Data storage and isolation
・Confirm server locations: the EU GDPR and Taiwan's personal data law have rules on cross-border transfers. Data stored on U.S. servers is not automatically compliant
・For Enterprise accounts, confirm there is logical isolation so your data is fully separated from other tenants
Liability for breach
・If a data breach occurs at the vendor, they must notify you within a set number of hours. 72 hours is a common industry standard
・Damages clauses for breach must be specific, not just wording like "make best efforts to prevent."
Audit rights
・Are you allowed to request records of the vendor's data processing?
・ISO 27001 or SOC 2 certification is a basic threshold. It means the vendor has passed a third-party information security audit
If the vendor's service terms are a public online document and cannot be customized for you, the only thing you can do is confirm whether the platform's usage policy meets your needs. Otherwise, you are handling customer data in a way that cannot be trusted
Major printing-industry SaaS tools, such as Adobe Creative Cloud and Canva Enterprise, have issued clear GDPR and personal data compliance statements in recent years. But those statements are not the same as an NDA. You only have real protection after signing an enterprise contract
A Compliance Checklist Before Introducing AI into the Company
This is the checklist I use when helping printing plants and design companies introduce AI workflows. It is not a theoretical framework. It comes from actual implementation work:
Before rollout
・Confirm the version of the AI platform's terms of use and its description of data usage
・Assess whether you need an enterprise version, API version, or local deployment, based on data sensitivity
・Confirm with legal whether existing customer contracts include clauses stating that customer data must not be handed to a third party for processing
Building internal rules
・Create an "AI-eligible data classification table," using the classification logic above as a reference
・Define which workflows may use AI and which are banned, such as prohibiting public AI throughout all VDP operations
・Set up employee training on AI usage at least once a year
Vendor management
・Require all AI tool vendors to provide a DPA, Data Processing Agreement
・Confirm that the vendor has ISO 27001 or SOC 2 certification
・Review updates to each vendor's privacy policy every year after signing
Daily operations
・Before pasting anything into AI, run a de-identification self-check: does this content include information that can identify a specific person or company?
・If there is any doubt, replace the sensitive parts before sending. Do not gamble
・After sensitive tasks are completed, clear the conversation history in the AI platform. Most platforms offer a manual deletion option
If your company takes on print jobs that require strong personal data protection, such as medical, financial, or government tender projects, it is better to work directly with a commercial printing provider like MINDS that has a complete compliance workflow. From design to final imposition, the work stays inside a controlled environment, reducing the chance of information security gaps
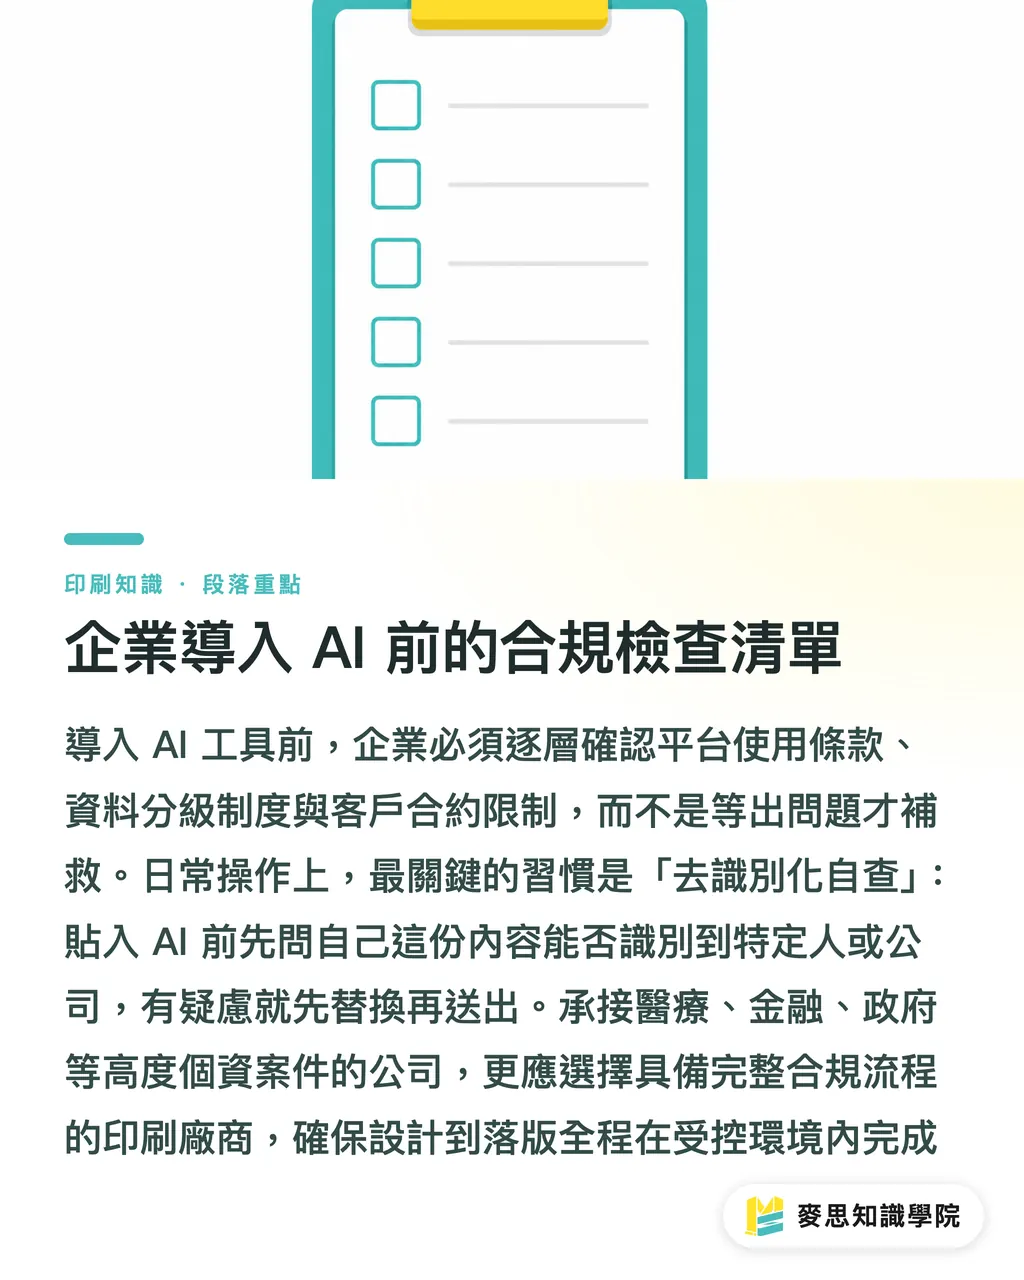
Key Takeaways
・The public version of ChatGPT may use your input data to train models by default. Enterprise and API versions clearly commit not to. Their compliance risks are not in the same league
・In Variable Data Printing (VDP), real customer lists should be fully isolated from AI tools from the moment they enter the workflow. Use only fake data for template testing
・The line for de-identification is this: after removal, the remaining data cannot be traced back to any real person or company. Changing only the name while keeping distinctive business details does not count
・When signing with an AI vendor, check four things: data use, server location, notification obligations, and audit rights. Without a DPA, you do not have real protection
・Internal AI usage rules cannot stay as slogans. The rule that public AI is banned for VDP must be written into the operating SOP before it counts as implemented
Further Thoughts
When it comes to compliance, the printing industry actually has an advantage over most industries, because we are already used to handling confidential customer materials: keeping design files confidential, preventing proofs from leaking, and keeping quotes private. These are basic professional habits in the field. Extending the same logic to AI tools is not difficult
The most practical next step is one thing: list every AI tool currently used in the company, then check one by one whether each is an enterprise version and whether a DPA has been signed. If any tool is being used through an employee's personal account, switch it to a company account now, or upgrade directly to Enterprise. This move is not complicated, but it can cut off 80% of the risk
Design companies and printing plants do not need to wait until something goes wrong before acting on AI compliance. Building a data classification table now and teaching employees what can and cannot be pasted into AI is far cheaper than fixing the damage later
FAQ
- What are the specific data security differences between the free version of ChatGPT and the enterprise version?
- The free version and Plus personal accounts allow OpenAI by default to use conversations to improve models, meaning the data enters the training pool. ChatGPT Enterprise clearly commits that it does not train models on customer input data, and data is encrypted both in transit and at rest. Put simply, with the personal version, your input may be seen and learned from by OpenAI. With the enterprise version, it will not
- Can customer lists for Variable Data Printing (VDP) be processed with AI tools?
- No. VDP customer lists usually contain personal data such as names, addresses, and phone numbers. Putting them directly into public AI tools violates the "specific purpose" principle under personal data protection law. The correct approach is to test templates with fake data, while real lists are processed only locally or inside a secure, controlled, end-to-end workflow
- Is replacing names enough for de-identification?
- No. The standard for de-identification is this: after removal, no one can infer the real individual or specific company from the remaining information. If you replace the name but keep a distinctive business description, such as "the largest manufacturer of this type in northern Taiwan," people in the industry may still identify the company. That is not true de-identification
- Which document matters most in a service contract with an AI vendor?
- The most important document is the DPA, or Data Processing Agreement. It clearly defines how the vendor processes, stores, and protects your data, as well as notification obligations and compensation terms if a breach occurs. If you only have a service contract or online terms, but no DPA, you effectively have no legal protection
- Is locally deployed AI always safer than cloud services?
- For data privacy, local deployment is indeed the safest option because the data never leaves your own environment, so there is no third-party server compliance issue. But security still depends on your own IT management. If internal servers lack proper access control and encryption, local deployment still carries risk. In practice, for small and midsize businesses, an enterprise cloud option such as Azure OpenAI Service may be easier to control if it comes with a complete DPA and security certifications
Related articles
The Print × AI weekly
The print and AI know-how designers, brands and enterprises can use before they commit — one email, every week
MINDS Free Tools
AI background removal, brand stamping, and a LINE sticker maker — free design tools, right in your browser, no upload.
MINDS Group
Need actual printing or gifting services?
From premium printing to online ordering and festive gifts — the MINDS Group sister brands take it from here.